http://www.tyan.com
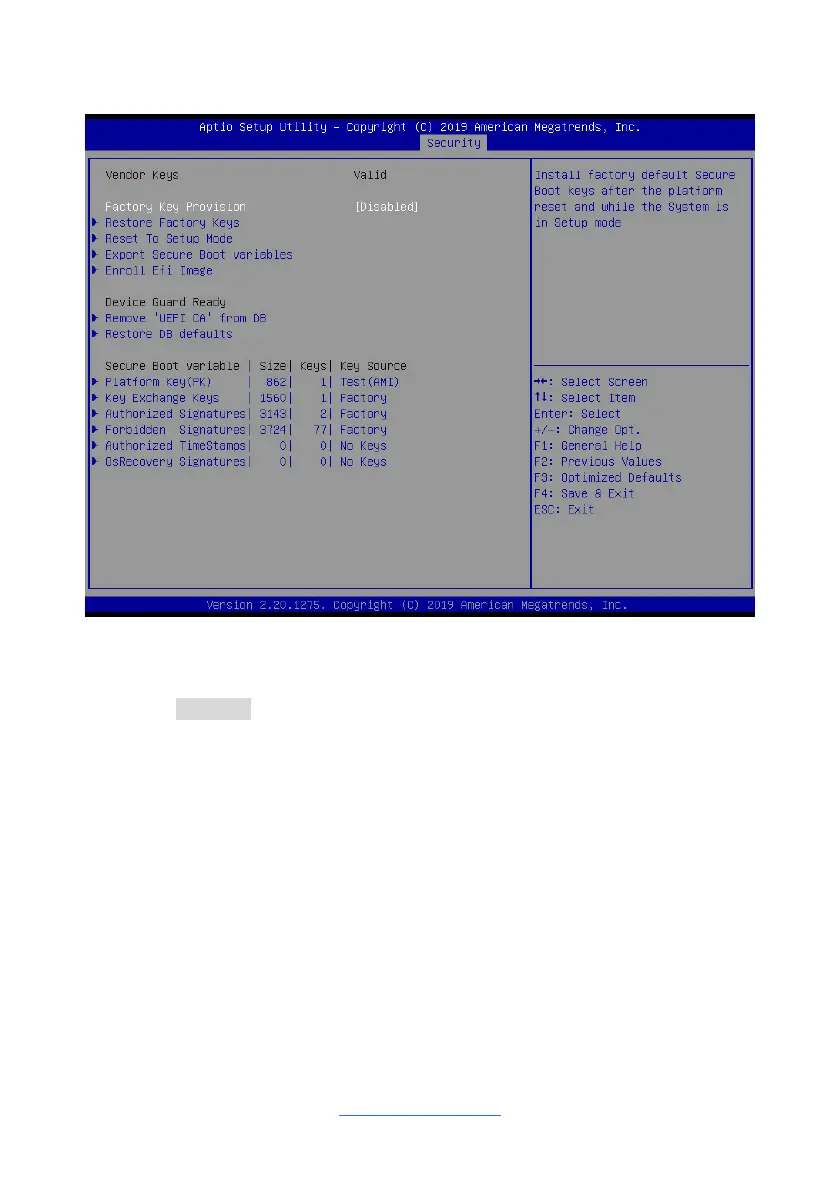
6.6.1.1 Key Management Configuration
Factory Key Provision
Install factory default Secure Boot keys after the platform reset and while the System
is in Setup mode
Disabled / Enabled
NOTE: The follow menu will be free when [Provision Factory Defaults] is set to
[Enabled].
Restore Factory Keys
Force System to User Mode. Install factory default Secure Boot key databases
Reset To Setup Mode
Delete all Secure Boot Key databases from NVRAM
Export Secure Boot variables
Copy NVRAM content of Secure Boot variables to files in a root folder on a file
system device
Enroll Efi Image
Allow the image to run in Secure Boot mode.
Enroll SHA256 hash of the binary into Autorized Signature Database (db)


 To Next Page