TEW-823DRU
32
© Copyright 2014 TRENDnet. All Rights Reserved.
ÍNote: In the Services Block Rule List secon, you can edit a rule by clicking in the
Edit column next to the rule you would like to edit. To delete the rule, click in the
Delete column next to the rule you would like to delete.
Block All Services
1 Log into your router management page (refer to “Log in to Management Page” on page 8).
2 Click on Advanced > Security > Access Control.
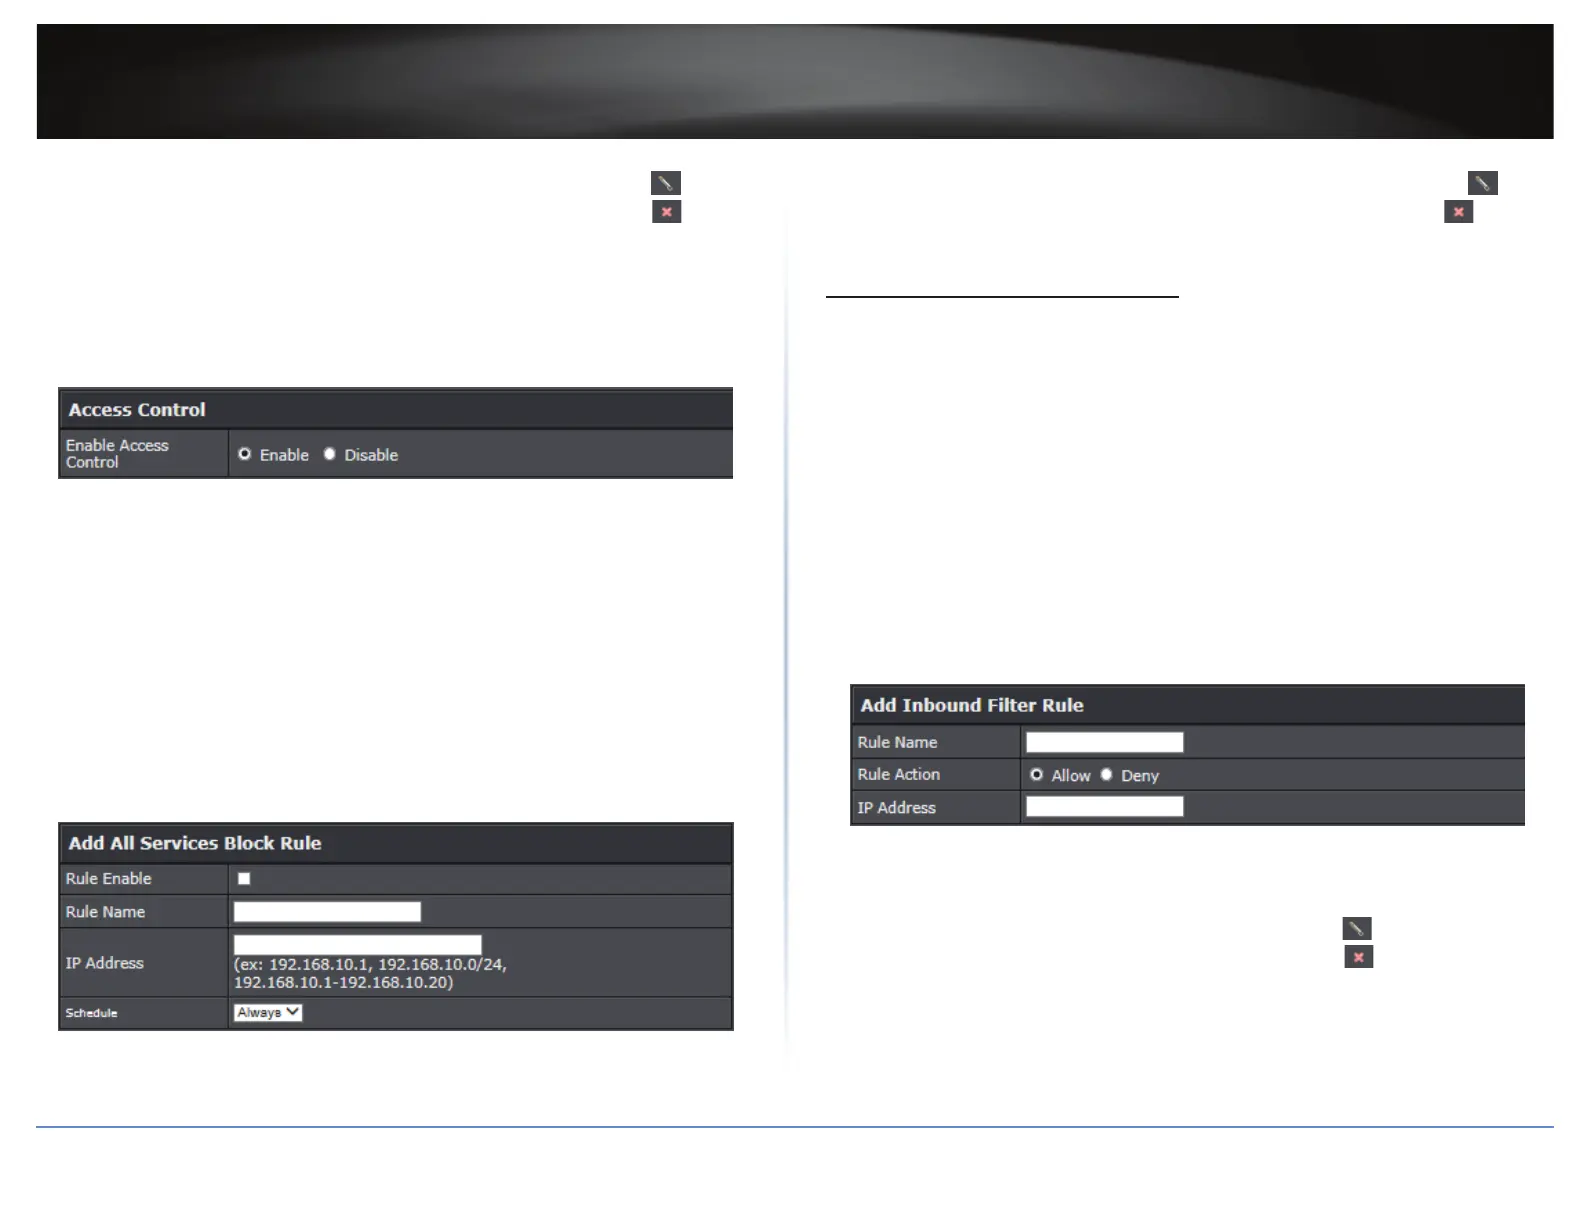
3 In Access Control secon, click the Enable opon.
4 In Add Services Block Rule secon, modify the following values:
Rule Enable: Checking this opon turns on the Protocol/IP Filter and unchecking
turns it o.
Rule Name: Enter a name for the Protocol/IP Filter.
IP Address: Enter the IP address or IP address range to apply the protocol/IP lter. For
example, 192.168.10.1, 192.168.10.0/24 or 192.168.10.1-192.168.10.30.
ÍNote: The lter will not be applied to IP addresses outside of the range specied.
Schedule (Oponal): Select the pre-dened schedule to apply. The lter will only be
acve during the me period dened in the pre-dened schedule.
ÍNote: Before applying scheduling, please ensure your Time sengs are congured
correctly and you have dened a schedule. Refer to “Set the Date and Time” on
page 42 and “Create Schedules” on page 30 to create a schedule.
5 Click Add to save the rule.
ÍNote: To discard the changes, click Reset.
ÍNote: In the All Services Block Rule List secon, you can edit a rule by clicking in the
Edit column next to the rule you would like to edit. To delete the rule, click in the
Delete column next to the rule you would like to delete.
Congure Inbound Filter Rules
Advanced > Security > Inbound Filter
Inbound Filters allows you to allow or deny a specic range of IP addresses. You can create
a predened range of IP addresses to apply to a specic feature.
ÍNote: You can apply a predened inbound lter to the following features:
ͳ Virtual Server
ͳ Gaming
ͳ Remote Management
1 Log into your router management page (refer to “Log in to Management Page” on page 8).
2 Click on Advanced > Security > Inbound Filter.
3 In Add Inbound Filter Rule, modify the following values:
Filter Name: Enter a name for the IP address range.
Rule Acon: Select Allow to allow the specied IP address range or Deny to deny the
specied IP address range.
IP Address: Enter the IP address. For example, 192.168.1.20-192.168.1.30.
4 Click Add to save the Inbound Filter.
ÍNote: To discard the changes, click Clear.
ÍNote: In the Inbound Filter List, you can edit a rule by clicking in the Edit column
next to the rule you would like to edit. To delete the rule, click in the Delete column
next to the rule you would like to delete.















 To Next Page