182
3-17-2. DHCP Snooping Entry
Function name:
DHCP Snooping Entry
Function description:
DHCP snooping Entry allows a switch to add the an trust DHCP server and 2
trust port to build the DHCP snooping available entry. This information can be
useful in tracking an IP address back to a physical port and enable or disable
the DHCP Option 82.
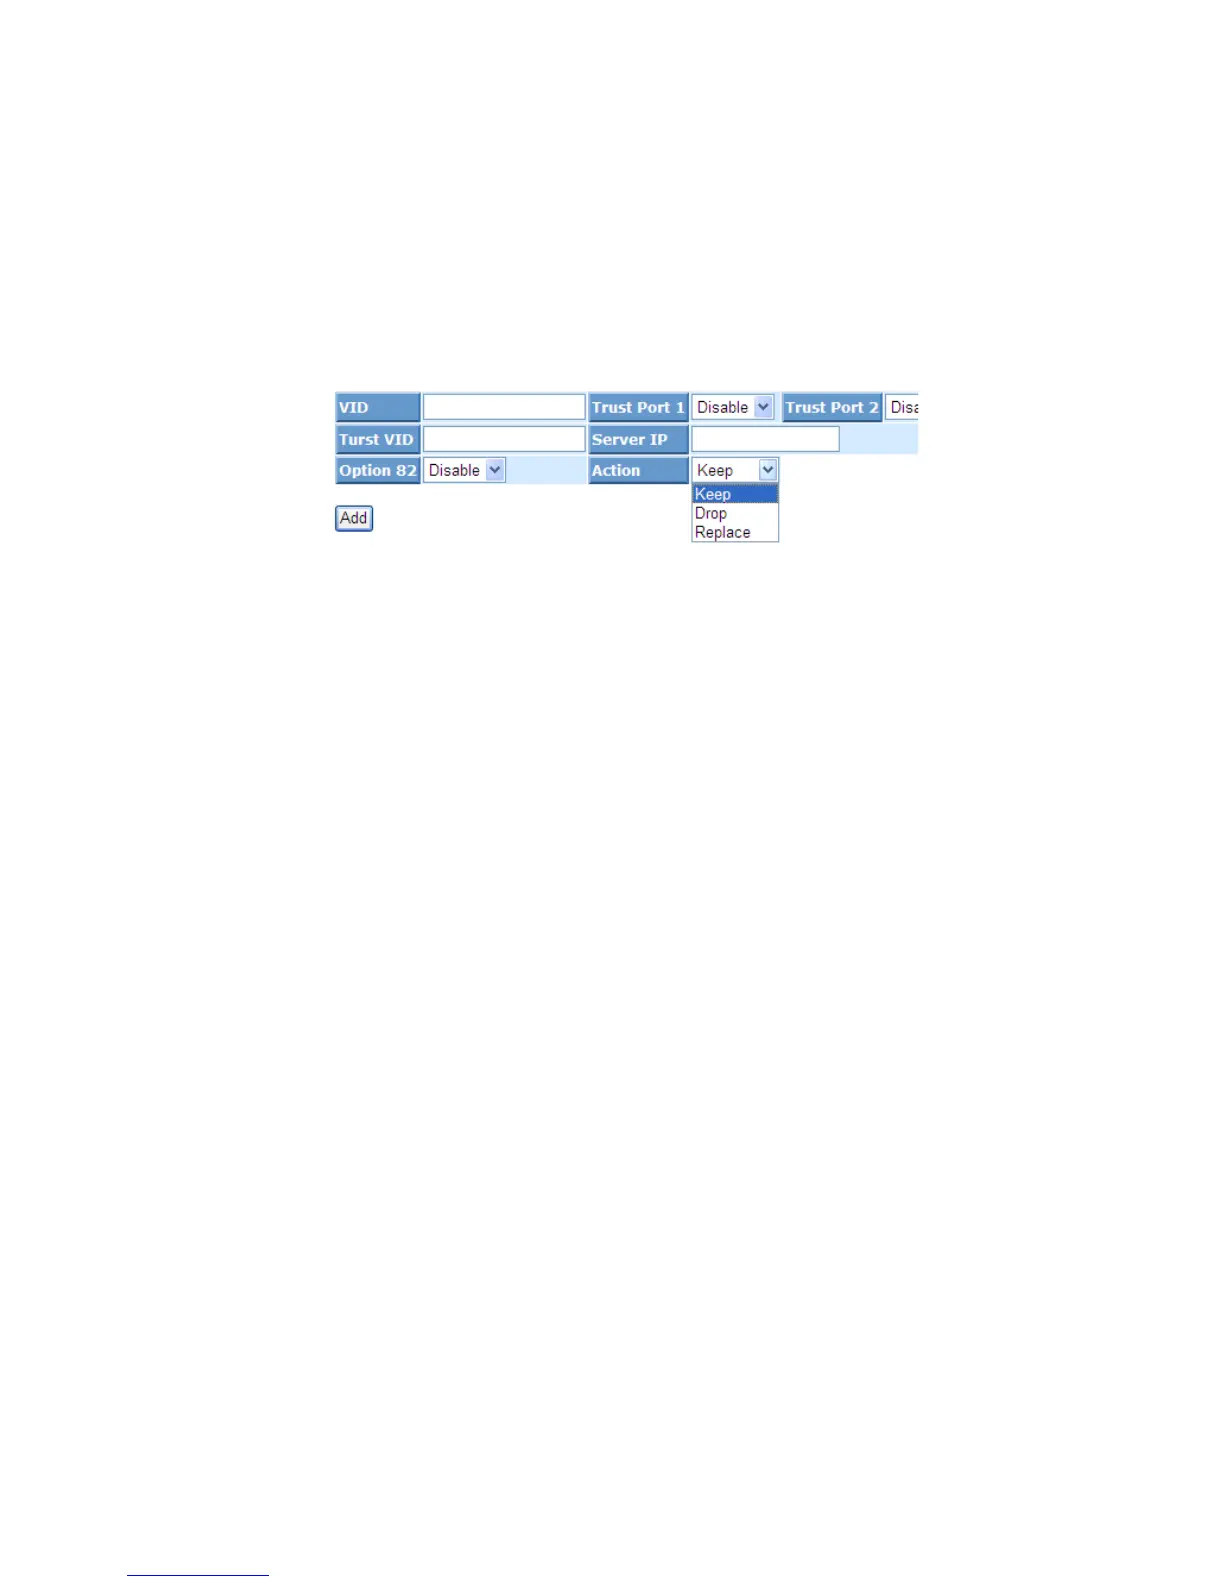
Fig. 3-17-1 DHCP Snooping State
Parameter description:
VID:When DHCP snooping is enabled, and enabled on the specified
VLAN, DHCP packet filtering will be performed on any un-trusted
ports within the VLAN. It set a available VLAN ID to enable the DHCP
snooping on VLAN interface.
Trust Port 1:If DHCP snooping is enabled globally, and also enabled on
the VLAN where the DHCP packet is received, all DHCP packets are
forwarded for a trusted por. It set a trust port 1. available port from 0
to 24. 0 is disabled.
Trust port 2 : It set a trust port 2. available port from 0 to 24. 0 is disabled.
Trust VID: It set a trust VLAN ID. available VID from 1 to 4094.
Server IP: It set a trust DHCP Server IP address for DHCP Snooping.
Option 82:It set the DHCP Option 82 function on the switch, default is
Disable.
Action:It set the switch when received a client DHCP request packet then
action for filtering. available action : keep/ drop / replace.
Note
:
Filtering rules are implemented as follows:
- If the DHCP snooping is disabled, all DHCP packets are forwarded.
- If DHCP snooping is enabled and also enabled on the VLAN where
the DHCP packet is received, all DHCP packets are forwarded for a
trusted port.
- If DHCP snooping is enabled and also enabled on the VLAN where
the DHCP packet is received, but the port is not trusted, it is


 To Next Page