ip-rule default
composite-operation deny
exit
exit
!
! Activate the crypto list and the access control list on the public
interface
!
interface fastethernet 10/3
ip crypto-group 901
ip access-group 301 in
ip access-group 302 out
exit
Checklist for configuring site-to-site IPSec VPN
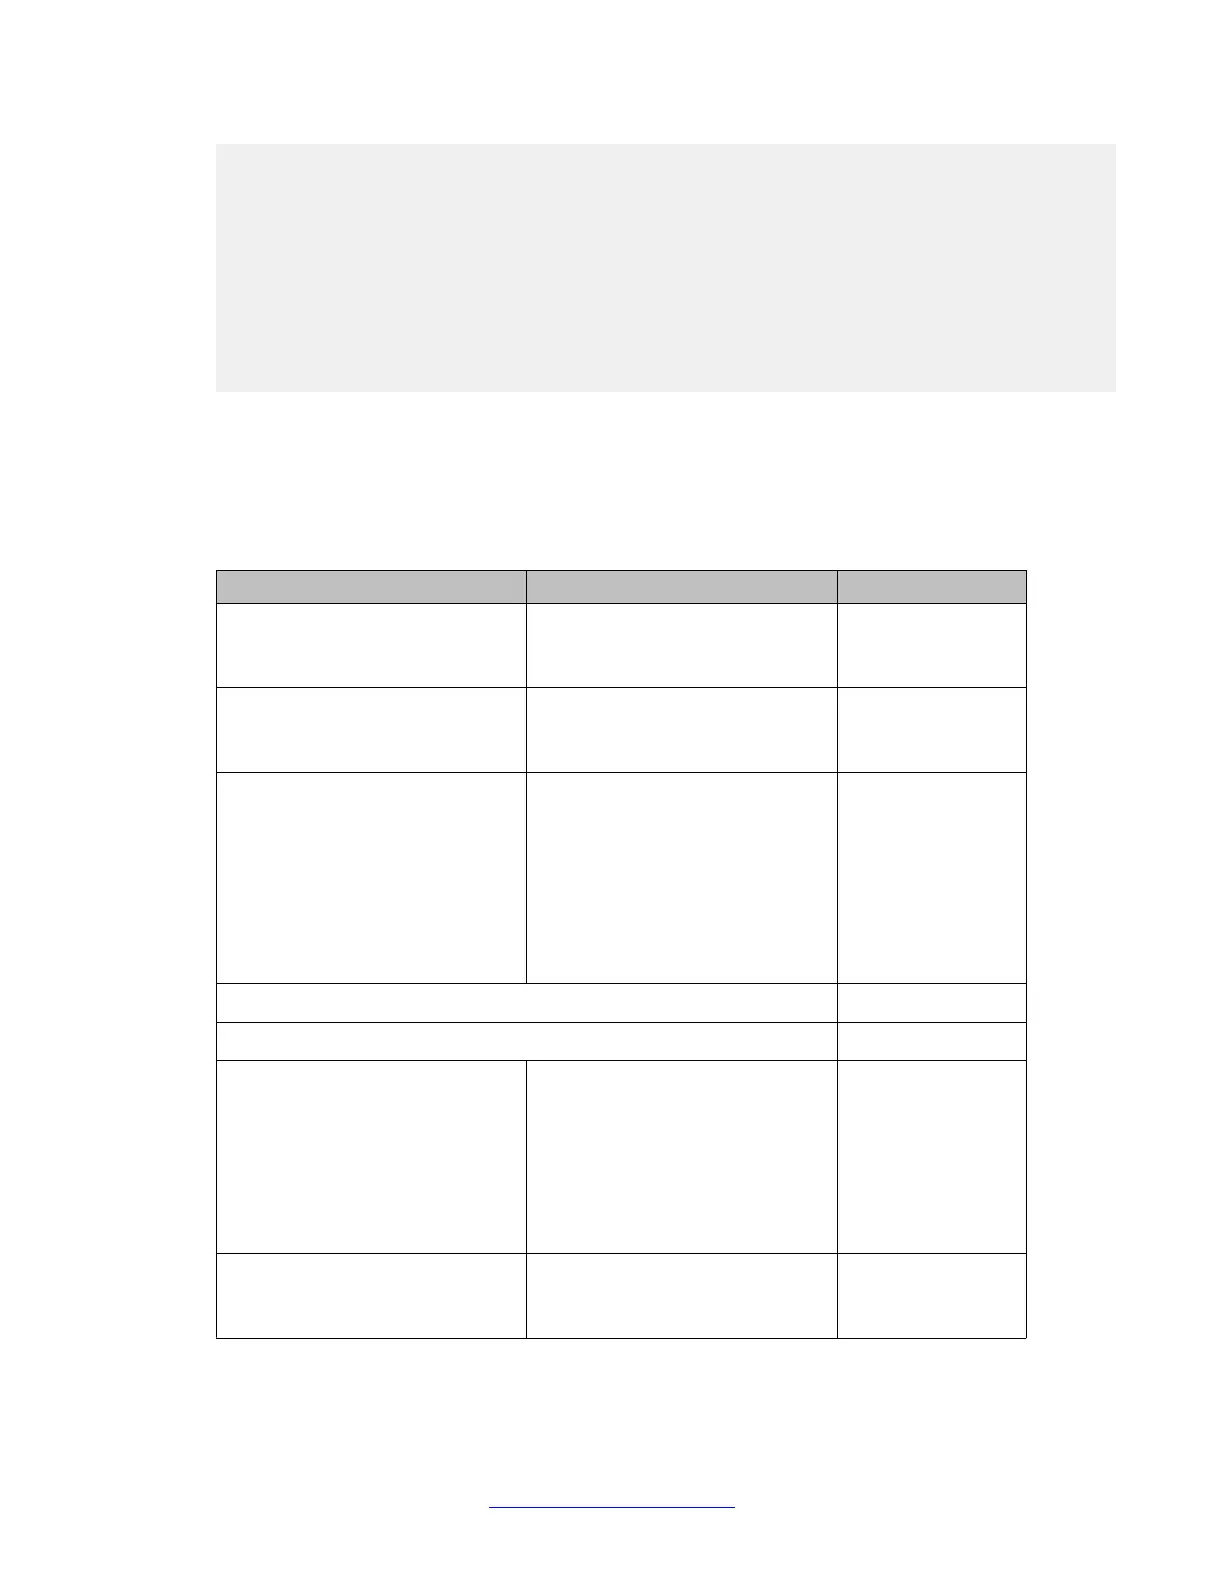
Use the following table to gather the information for simple Gateway site-to-site IPSec VPN.
Parameter Possible values Actual value
1. Type of connection to the ISP
• ADSL
• Cable Modem
2. VPN Interface
• FastEthernet10/3
• Serial port X/Y
3. VPN Local IP Address Type:
• Static
– If static, provide:
IP Address
Mask
Next-hop Router
• Dynamic (DHCP/PPPoE)
4. Coordinating with the VPN Remote peer
a.) VPN IKE (Control) Phase 1 Parameters
— Encryption
• des
• 3des
• aes
• aes-192
• aes-256
— Authentication Hash
• sha
• md5
IPSec VPN
548 Administering Avaya G430 Branch Gateway October 2013
Comments? infodev@avaya.com


 To Next Page