Advanced Threat Prevention Engine Settings
Quantum Spark 1500, 1600, and 1800 Appliances R81.10.X Locally Managed Administration Guide|209
In Threat Emulation, each file is run in the Check Point Public ThreatCloud to see if the file is malicious. The
verdict is returned to the gateway.
You can change the emulator location to a local private SandBlast appliance in the Advanced Settings
page.
You must first enable the Threat Emulation blade and then configure it for remote emulation.
To enable the Remote Private Cloud Threat Emulation emulator:
1. Go to Device > Advanced Settings.
2. Search for Threat Prevention Threat Emulation policy - Emulation location.
3. Select Emulation is done on remote (private) SandBlast.
4. Add or update the emulator IP address.
5. Click Apply
To disable the Remote Private Cloud Threat Emulation emulator:
1. Go to Device > Advanced Settings.
2. Search for Threat Prevention Threat Emulation policy - Emulation location.
3. Select Emulation is done on Public ThreatCloud.
4. Click Apply
To configure multiple remote emulators, you must use CLI commands.
For more information on Threat Emulation, see the
Threat Emulation video
on the
Small Business Security
video channel
.
To enable Detect-only mode:
Select the checkbox.
User Messages
You can customize messages for protection types set with the Ask action. When traffic is matched for a
protection type that is set to Ask, the user's internet browser shows the message in a new window.
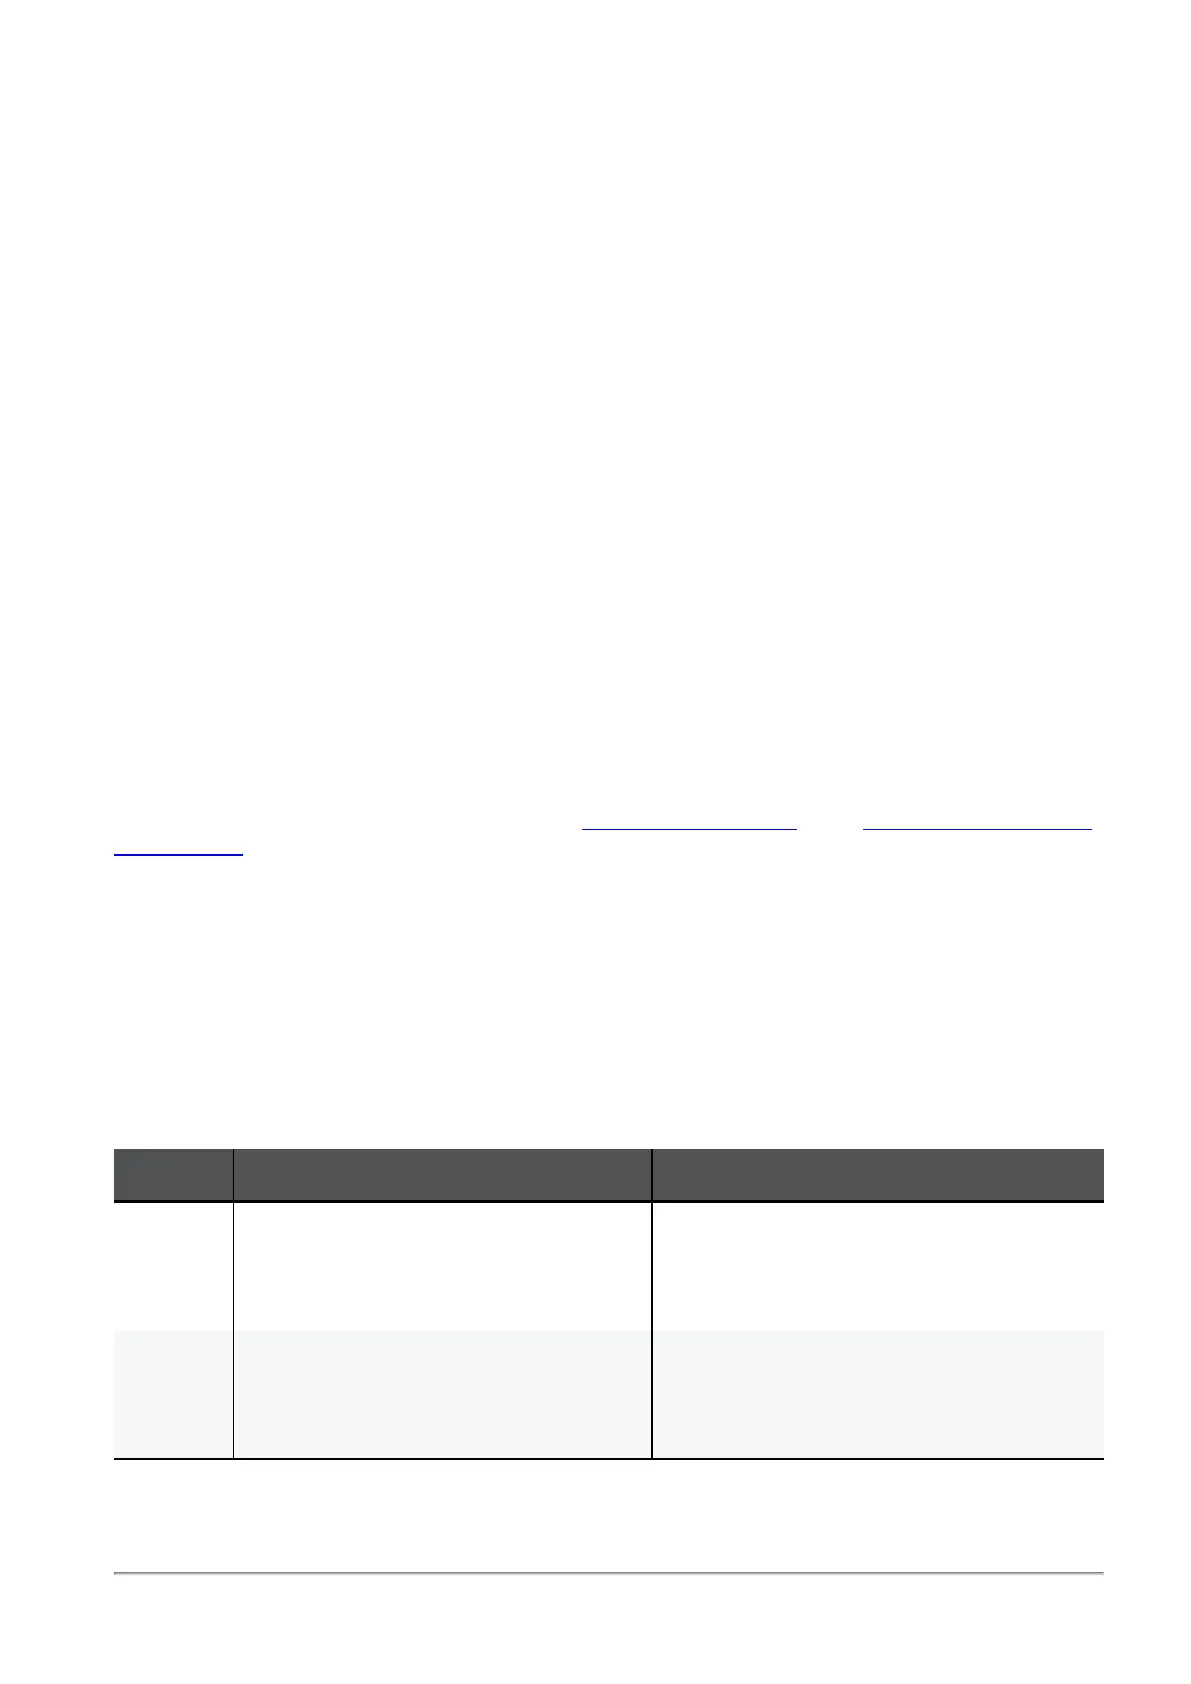
These are the Ask options and their related notifications:
Option Anti-Virus Notification Anti-Bot Notification
Ask Shows a message to users and asks them
if they want to continue to access a site or
download a file that was classified as
malicious.
Shows a message to users and notifies them
that their computer is trying to access a
malicious server.
Block Shows a message to users and blocks the
site.
Anti-Bot blocks background processes. If a
specified operation from a browser to a
malicious server is blocked, a message is
shown to the user.









 To Next Page