Administrator’s Handbook
60
Link: Packet Filter
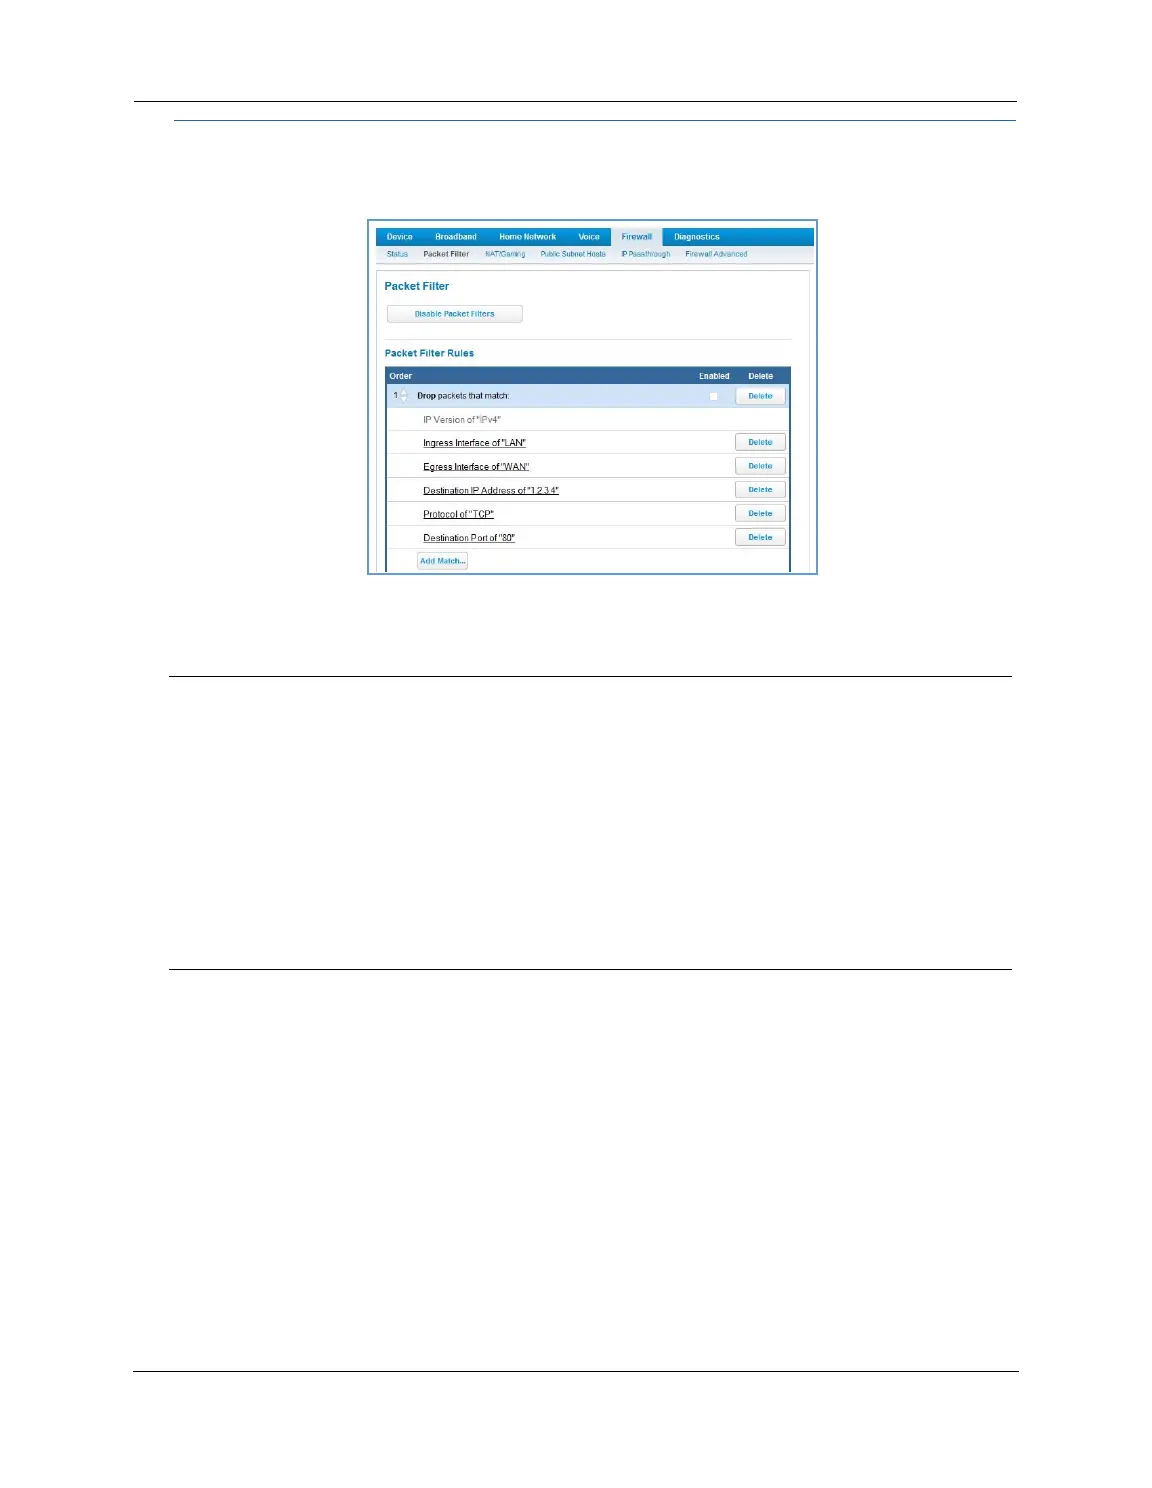
When you click the Packet Filter link, the Packet Filter page appears.
Security should be a high priority for anyone administering a network connected to the Internet. Using packet
filters to control network communications can greatly improve your network’s security. The Packet Filter
engine allows creation of a maximum of eight filtersets. Each filterset can have up to eight rules configured.
ARRIS’s packet filters are designed to provide security for the Internet connections made to and from your
network. You can customize the
NVG599 device’s filtersets for a variety of packet filtering applications. Typically,
you use filters to selectively admit or refuse TCP/IP connections from certain remote networks and specific
hosts. You will also use filters to screen particular types of connections. This is commonly called firewalling
your network.
Before creating filtersets, you should read the next few sections to learn more about how these powerful
security tools work.
WARNING:
Before attempting to configure filters and filtersets, please read and understand this entire section thor-
oughly. The ARRIS NVG599 device incorporating NAT has advanced security features built in. Improperly add-
ing filters and filtersets increases the possibility of loss of communication with the device and the Internet.
Never attempt to configure filters unless you are local to the NVG599 device.
Although using filtersets can enhance network security, there are disadvantages:
• Filters are complex. Combining them in filtersets introduces subtle interactions, increasing the likelihood of
implementation errors.
• Enabling a large number of filters can have a negative impact on performance. Processing of packets will
take longer if they have to go through many checkpoints in addition to NAT.
• Too much reliance on packet filters can cause too little reliance on other security methods. Filtersets are
not a substitute for password protection, effective safeguarding of passwords, and general awareness of how
your network may be vulnerable.



 To Next Page