Active Directory Authentication
R81 Harmony Endpoint Server Administration Guide|176
Active Directory Authentication
Endpoint Security Active Directory
Authentication
When an Endpoint Security client connects to the Endpoint Security Management Server, an
authentication process identifies the endpoint client and the user currently working on that
computer.
The Endpoint Security system can function in these authentication modes:
n
Unauthenticated mode - Client computers and the users on those computers are not
authenticated when they connect to the Endpoint Security Management Server. They
are trusted "by name". This operation mode is recommended for evaluation purposes
only.
n
Strong Authentication mode - Client computers and the users on those computers are
authenticated with the Endpoint Security Management Server when they connect to the
Endpoint Security Management Server. The authentication is done by the Active
Directory server using the industry-standard Kerberos protocol. This option is only
available for endpoints that are part of Active Directory.
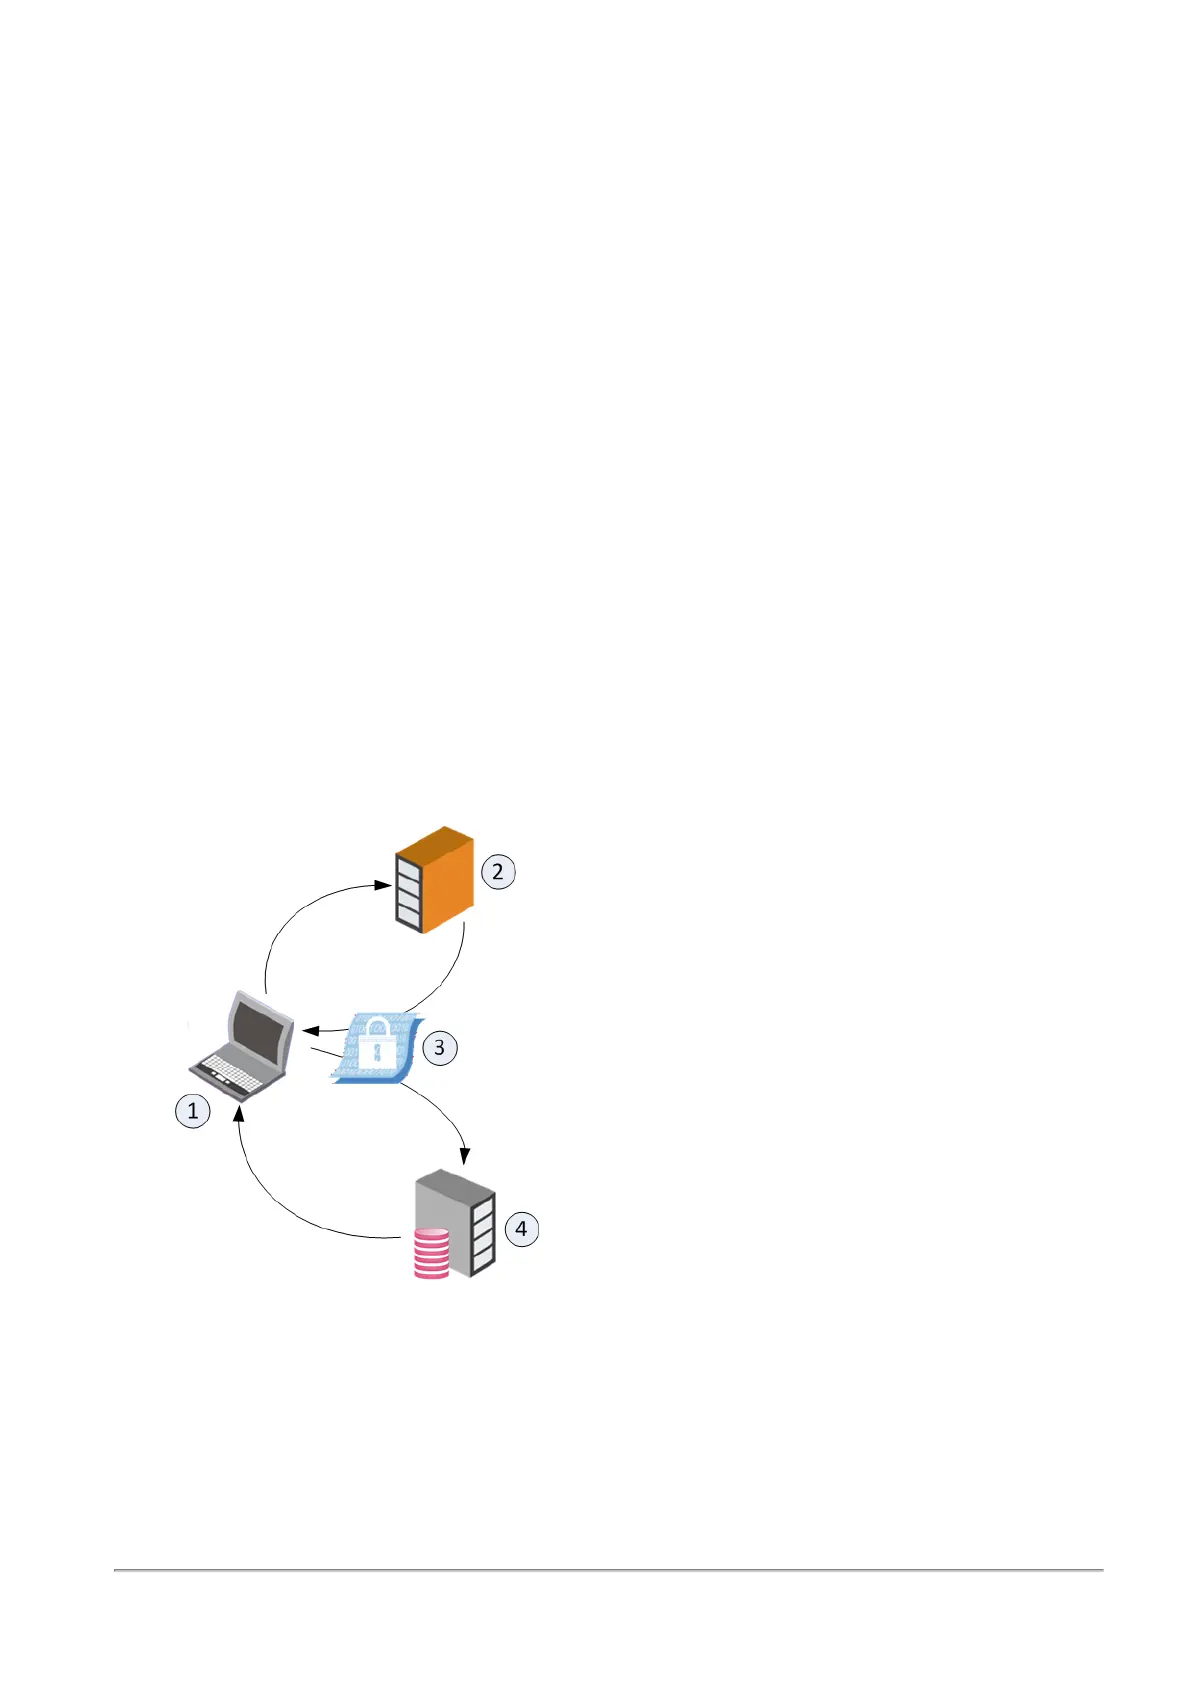
The authentication process:
1. The Endpoint Security client (1) requests an authentication ticket from the Active
Directory server (2).
2. The Active Directory server sends the ticket (3) to the client (1).
3. The client sends the ticket to the Endpoint Security Management Server (4).














 To Next Page