Ensuring that Windows Server Updates Are Installed
R81 Harmony Endpoint Server Administration Guide|369
Ensuring that Windows Server Updates Are Installed
Windows Server Update Services (WSUS) allows administrators to deploy the latest Microsoft
product updates.The WSUScompliance check ensures that Windows update are installed on
the Endpoint Security client computer. You can restrict network access of the client computer if
Windows updates have not been installed within a specified number of days. Alternatively, you
can warn the user by means of a pop-up message without restricting access, or log the non-
compliance event without restricting or informing the user
To configure the WSUScompliance check:
1. In the Policy tab Compliance rule, right-click the Windows Server Update Services
action
2. Select one of the following preset actions. An action happens if Windows updates have
not been installed on the Endpoint Security client computer for a specified number of
days (90 days by default):
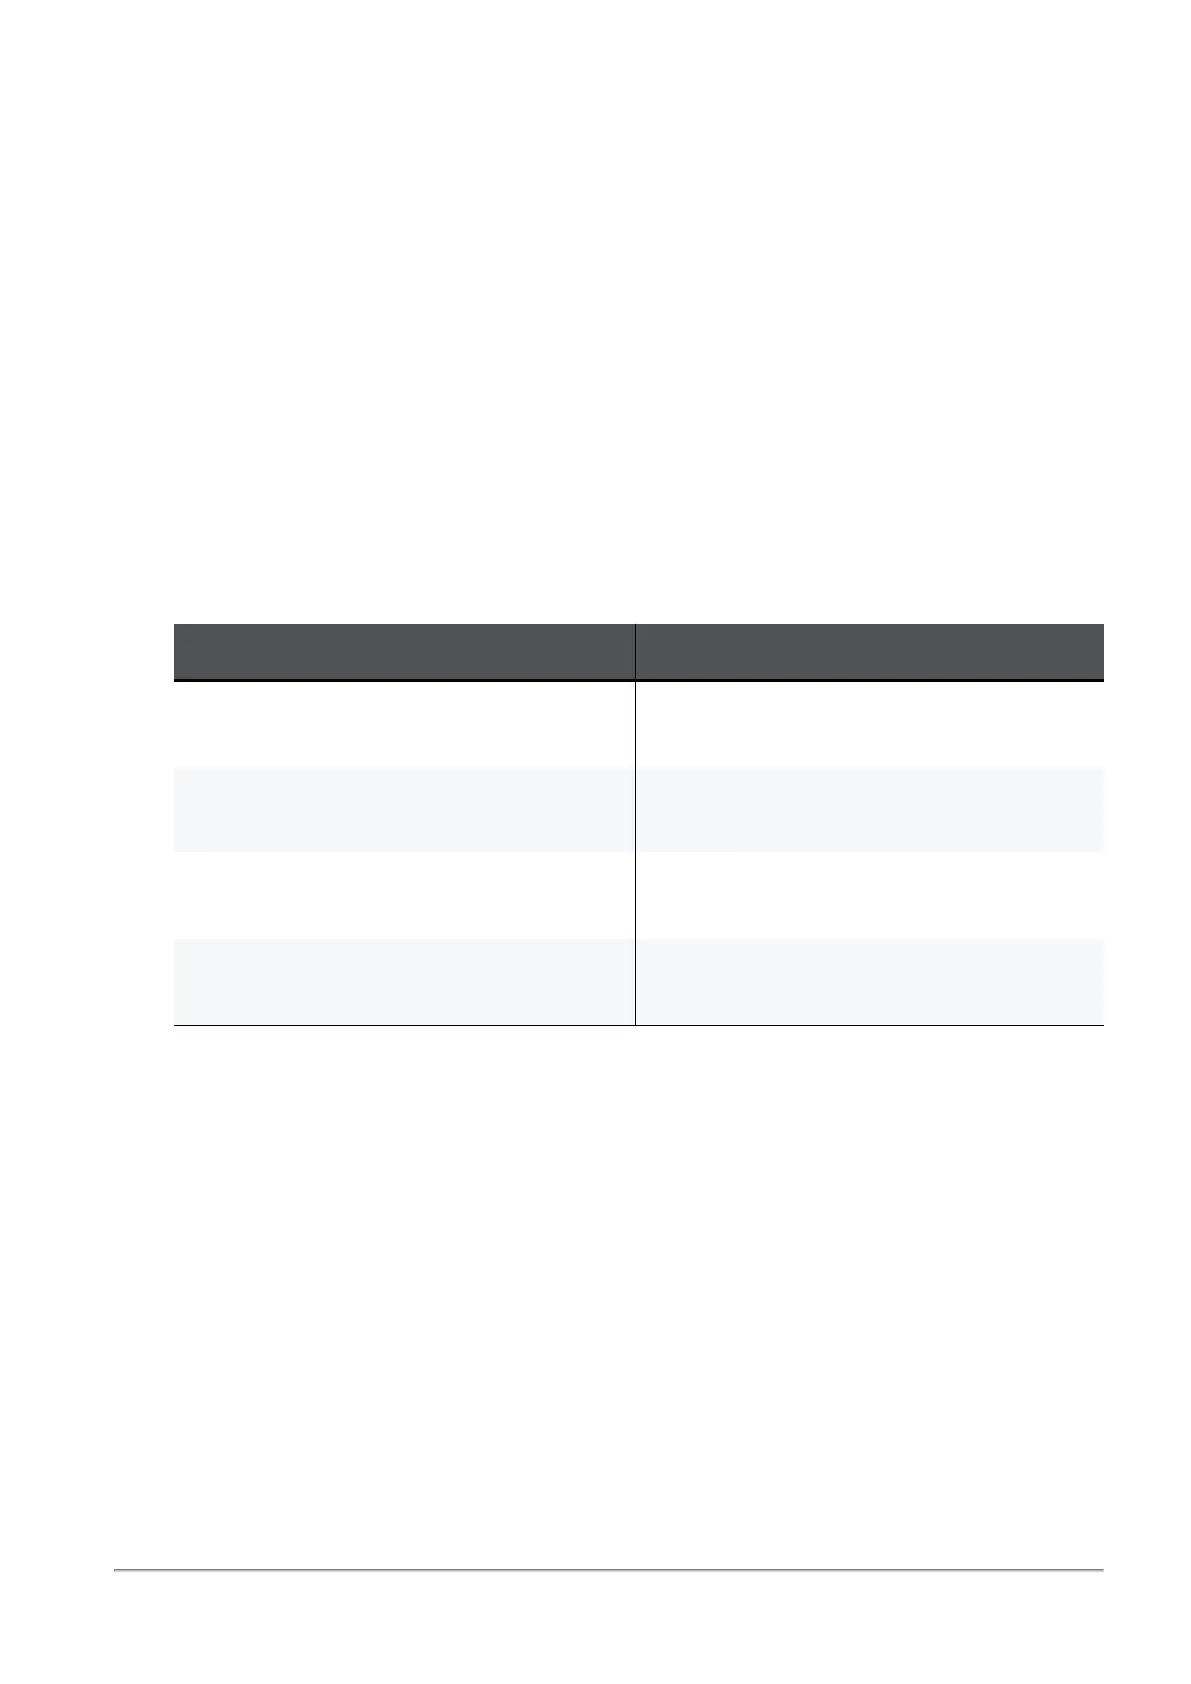
Preset Action Meaning
Restrict if Windows Server Updates are
not installed
Restrict the network access of the user.
Observe Windows Server Update
Services
Create a log, and show a warning
message to the user.
Monitor Windows Server Update
Services
Create a log. The user is not notified.
Do not check Windows Server Update
Services
No compliance check. This is the default.
3. Optional: The compliance check makes sure that the Windows updates have been
installed within a specified number of days (90 by default). To change the number of
days,
a. Right-click the Windows Server Update Services action.
b. Select Edit Shared Action.
c. Change the number of days in Windows updates must be installed within.


 To Next Page