Active Directory Authentication
R81 Harmony Endpoint Server Administration Guide|180
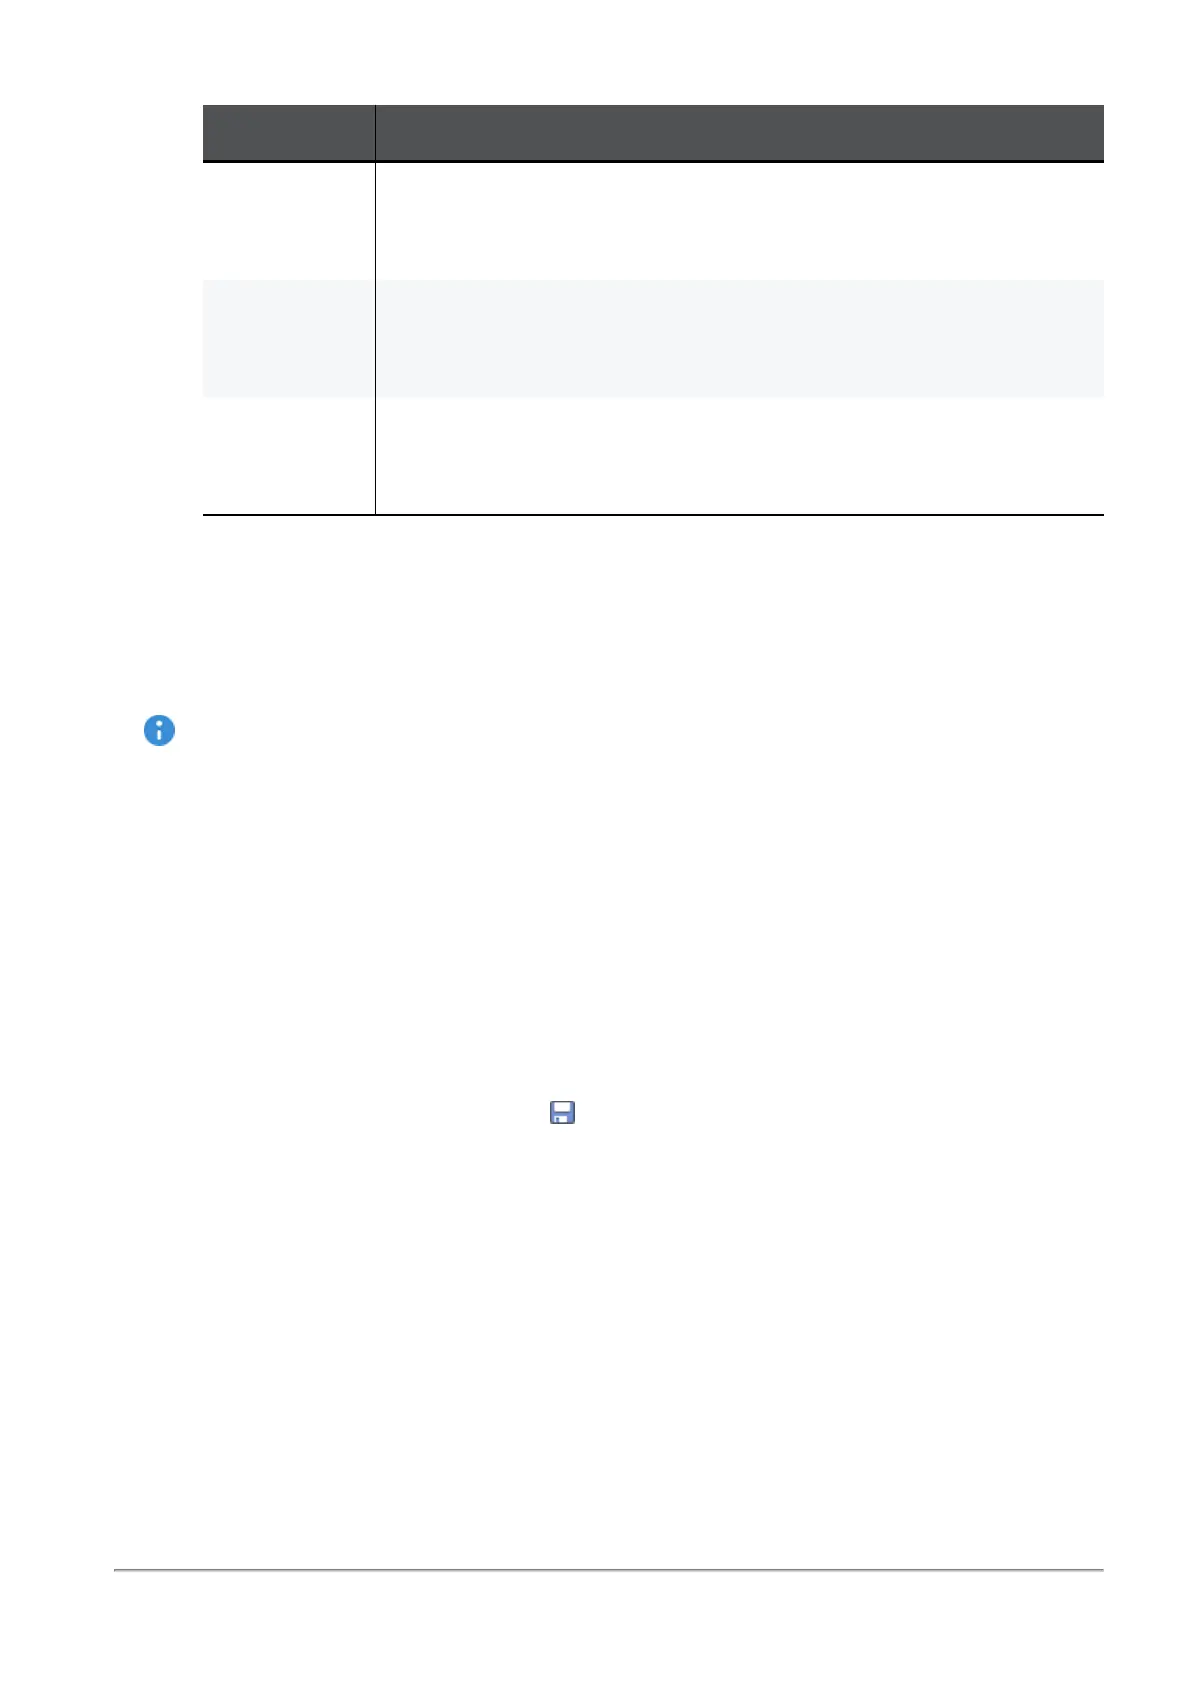
Field Description
Version Key Enter the version number according to the Active Directory output
in the vno field.
For example: 7
Encryption
method
Select the encryption method according to the Active Directory
output in the etype field.
For example: RC4-HMAC
Password Enter (and confirm) the password of the Active Directory Domain
Admin user you created for Endpoint Security use.
For example: 123456
4. Click OK.
5. When you are ready to work in Strong Authentication mode, select Work in
authenticated mode in the Authentication Settings Properties window.
6. Click OK.
Important - After turning on Strong Authentication, wait one minute before initiating
any client operations.
It will take time for the clients and the Endpoint Security Management Server to
synchronize. During this time, the environment will remain unauthenticated, and
some operations will fail. The exact amount of time depends on the
synchronization interval (see
"Active Directory Scanner" on page93
).
Step 3 of 3: Save Changes
After you have finished configuring strong authentication for Active Directory, save your
changes.
1. Go to the Policy tab of SmartEndpoint.
2.
In the Policy Toolbar, click Save .
UPN Suffixes and Domain Names
The User Principal Name (UPN) is the username in "email format" for use in Windows Active
Directory (AD). The user's personal username is separated from a domain name by the "@"
sign.
UPN suffixes are part of AD logon names. For example, if the logon name is
administrator@ad.example.com, the part of the name to the right of the ampersand is
known as the UPN suffix. In this case ad.example.com


 To Next Page