Using Tunnel Switching
Firebox Vclass User Guide 325
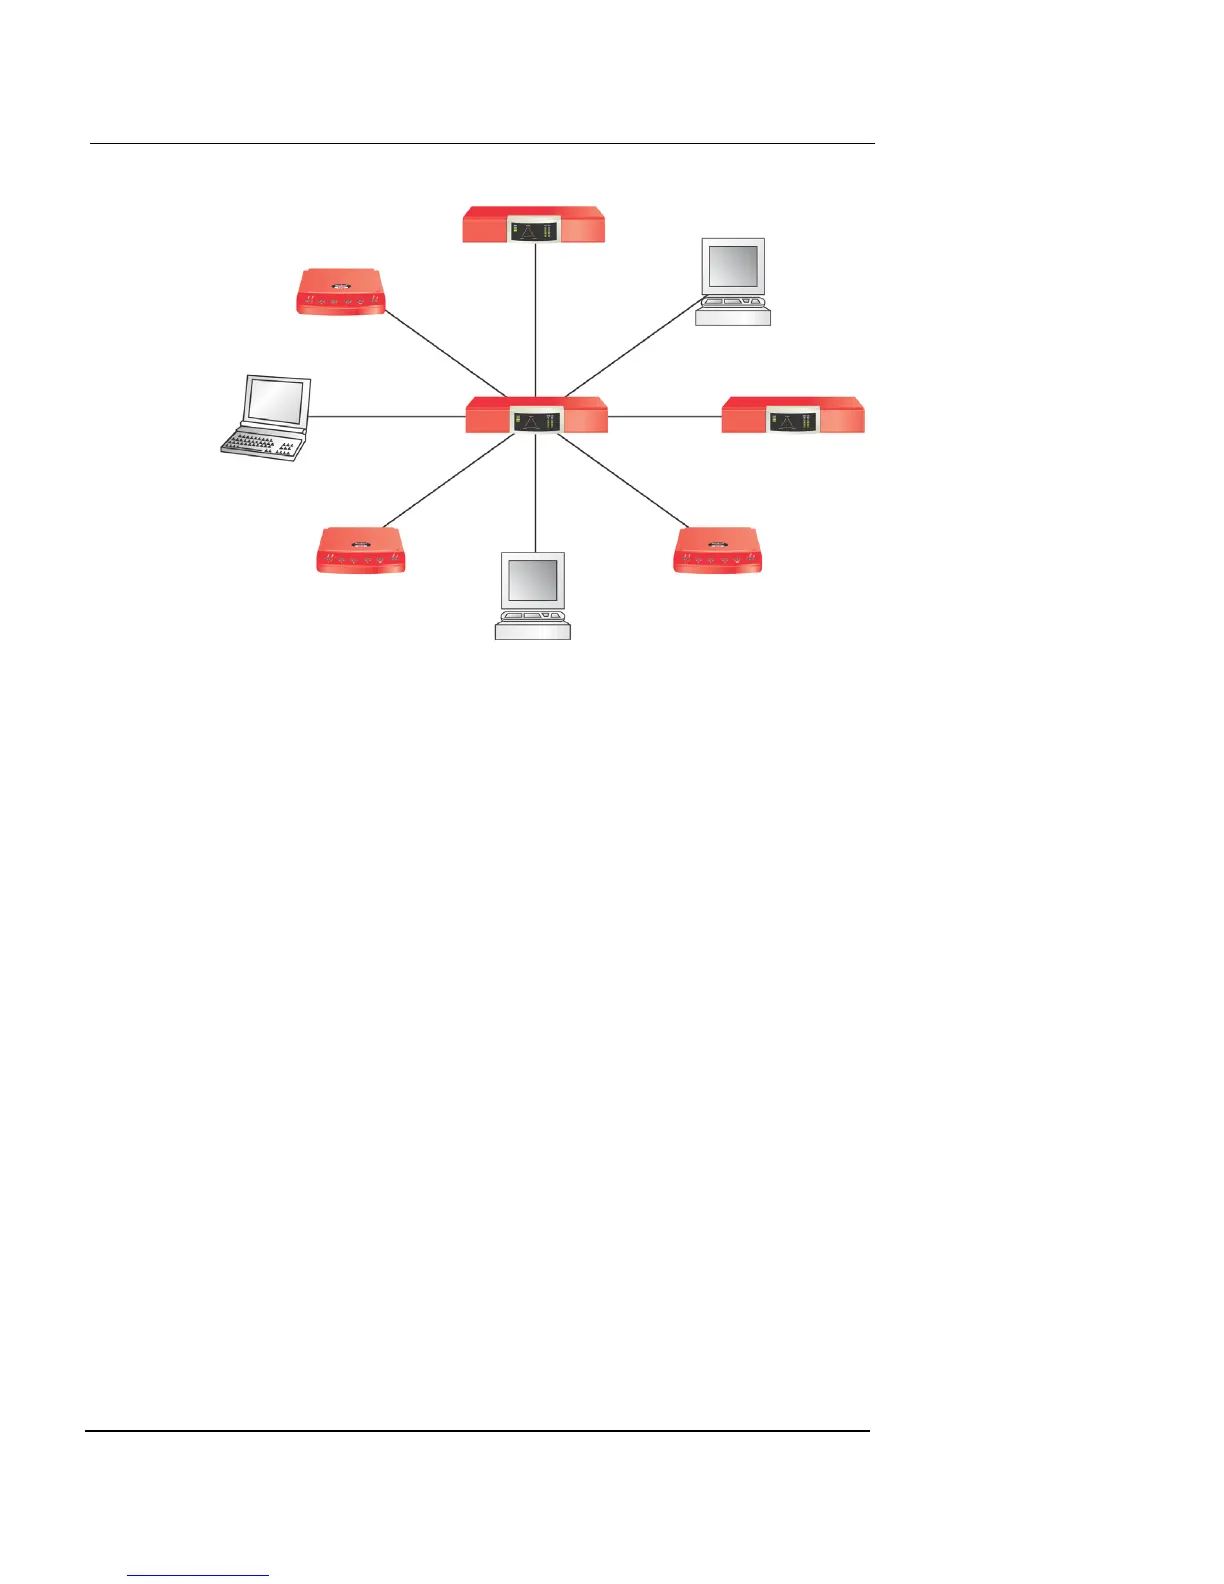
To make such a hub-and-spoke topology effective and effi-
cient, Firebox Vclass appliances provide tunnel switching
capabilities. Such a setup means that Site A can communi-
cate with site B by sending traffic to the central office,
which then switches this traffic from one tunnel (site A /
central office) to another tunnel (site B / central office). All
tunnel switching is performed by the Firebox Vclass appli-
ance, which prevents any degradation of network perfor-
mance.
The greatest benefit gained from tunnel switching is the
reduced cost of managing corporate VPNs. If a new branch
office is added to the corporate VPN network, the adminis-
trator only needs to add a new policy in the Firebox Vclass
appliance at headquarters. No additional configuration is
needed for the branch offices.
Before you enable tunnel switching, make sure you have:
• Certificates for both ends of the IKE exchange, if RSA
or DSS authentication is used.
• Agreements on other exchange parameters.













 To Next Page