AES Functional Description
www.ti.com
624
SWRU543–January 2019
Submit Documentation Feedback
Copyright © 2019, Texas Instruments Incorporated
Advance Encryption Standard Accelerator (AES)
GCM Operation
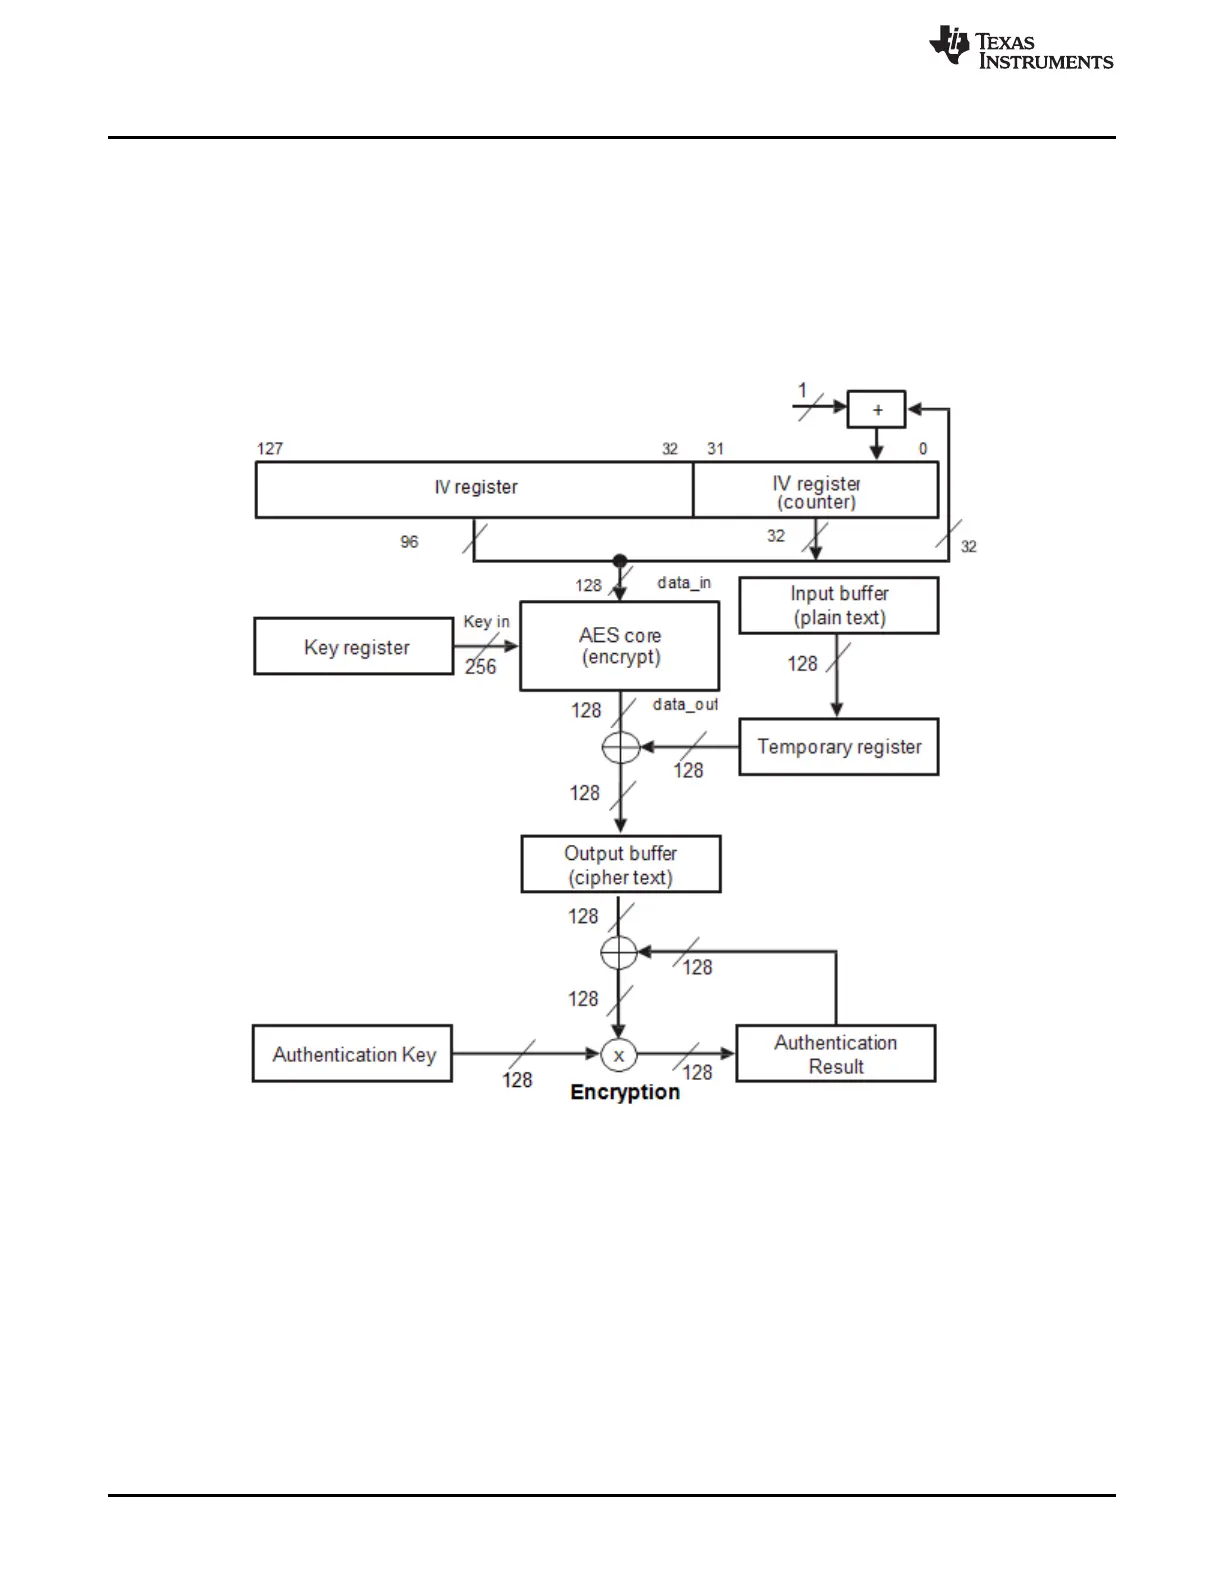
Figure 17-10 shows one round of a GCM operation for encryption and decryption. A 32-bit counter is used
as IV (as it is for CTR mode). The data is encrypted in the same way as in CTR mode, by XORing the
cryptographic core output with the input. After the encryption/decryption, the ciphertext is XORed with the
intermediate authentication result. The XORed result is used as input for the polynomial multiplication to
create the next (intermediate) authentication result. For more information about the GCM protocol, see
GCM Protocol Operation in Section 17.2.3.2.
Figure 17-10. AES - GCM Operation





 To Next Page